You can use an ADFS SAML connection to provide single sign-on for your users to log into Wixie.
To set up an SAML connection between an ADFS identity provider and Wixie, metadata must be exchanged between the servers. Users must exist in Wixie that match the Name-ID attributes being sent by the identity provider.
From the ADFS administration console, choose "Relying Party Trusts".
Choose "Add a new relying party trust".
Using the wizard, insert the following into the metadata URL: https://www.wixie.com/saml_sso/module.php/saml/sp/metadata.php/wixie-dynamic
Choose "Edit Claim Rules" (opened automatically by the wizard) to ensure Name-ID information is sent.
As an example, add two rules: one to retrieve a user’s LDAP id, and one to convert the id into SAML format.
Rule 1:
Rule 2:
Get the IdP metdata for the ADF instance. This can often be found at: https://server name/federationmetadata/2007-06/federationmetadata.xml
Log in to your organization’s admin account.
Click the Accounts tab.
Click the SAML radio button in the "How do you want to authenticate users?" section.
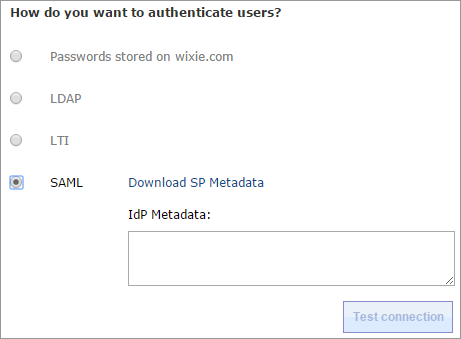
Paste the IdP metadata XML into the SAML IdP Metadata field.
Click the Test Connection button to confirm the connection has been created.
Follow us on:


Wixie
Resources